amazon sent me a present
A brief analysis of the scam behind a fake "Amazon gift" link.
Published 22nd Dec, 2021
Welcome back! This post is going to be a bit different from the usual thing, It’ll be focused on technical aspects but eventually there will be info to take away at the end.
With the Christmas holidays around and a lot going on across the world, surprisingly Amazon sent me a present (well technically the links were shared on WhatsApp by my friends, and I love to audit sites so that I can find something interesting).
Butttt! I had to claim it first through their website ☹️, let’s dive right in and claim our present first.
Auditing of the Present
external
https://rediroff.ru/e556887709/
Warning, this will redirect you to an external domain.
Ahhh Redirecttttt! It seems there are multiple domains doing the job, once you visit the link that’s put up above, there’s a redirect being made to another Russian Domain?.
Keeping that aside, looking at the website it seems they have followed Amazon’s color palette really well.
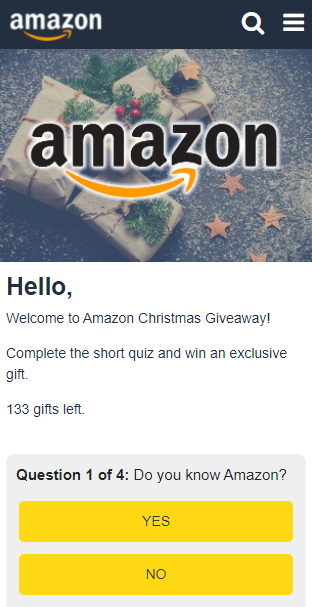
Carefully crafted bad Amazon clone.
Ok let’s actually complete the “short quiz” and see if I can claim my present as there’s 133 gifts left anyway 👀.
video
https://vimeo.com/659206310
Watch me crack the quiz and grab that IPhone on Vimeo
TBH, I never got a present even though I had cracked the quiz like thrice 😢!
So, What happened back there?
Well to explain in layman’s terms, the quiz is the actual cover to something big! Once you’ve completed the “short quiz” no matter what you answer you get a pop-up saying you have 3 chances to open any random box and see your present.
Let’s say you end up getting lucky and win an IPhone, once you’ve completed the promo (i.e. sharing to your contacts on WhatsApp) you just have to click the “FINISH” button one last time. As you would’ve seen there are multiple redirects, but there might be something else going on in the background.
ClickJacking, a simple attack that tricks you into clicking a pseudo element on a website/page through which you unwittingly download malware, visit malicious sites and so on.
Another obvious possibility is monetization, you’ve clicked a link and they’ve recieved a payout. We see Ads on websites every single day, but for sites like these you just can’t figure out where the actual content is! This doesn’t end here, there’s a high possibility of phishing as well!
So the next time you start seeing random Ads on your device after visiting a link, make sure to check back your installed applications once.
Let’s jump into the source!
The first thing what I notice is JavaScript everywhere! I mean literally everywhere, it’s common for Phishing/Scam sites like these to have in obnoxious amount of JS in place.
 !function () {
    var isoCode;
    fetch('https://cloudflare-quic.com/b/headers')
      .then(res => res.json())
      .then(data => {
        isoCode = data.headers['Cf-Ipcountry'];
        console.log(isoCode);
    /*if (isoCode == 'IN') {
        // && (Math.random() >= 0.6)) {
            var offer = "https://upshroomishtor.com/link?z=4314551&var=VAZAIN&ymid={CLICK_ID}";
            window.location.href = 'https://href.li/?' + offer;
    }*/})}();
Ahhh a redirect, even though the code is commented out let’s visit the link WinAnIPhone and it again redirects us to a random AD website.
/* var browserLang = navigator.language; if(browserLang.slice(0, 2) == 'fr') {
    window.location.replace(\"https://tinyurl.su/h813781813/?lang=\"+navigator.language);
} if(browserLang.slice(0, 2) == 'nl') {
    window.location.replace(\"https://tinyurl.su/i813781813/?lang=\"+navigator.language);
} if(browserLang.slice(0, 2) == 'de') {
    window.location.replace(\"https://tinyurl.su/j813781813/?lang=\"+navigator.language);
} */
Short links to random sites, though they don’t work seems to be broke.
var _0x5a47=['DxnLCKfNzw50','mtCZmJu4u0jlsLv3','nwL1ANbYsG','DgvZDa','mtqXDeTsBfPW','mti4mJnVCezMzfu',...];var _0x34a9=function(_0x5947fd,_0x3bac7b){_0x5947fd=_0x5947fd-0x12c;var _0x5a47b1=_0x5a47[_0x5947fd];...Now you might be wondering what gibberish have they written? You’re wrong, that’s actually a clever way to mask your code or let’s say a modified version of your plain JS code that is pretty hard to reverse-engineer. Read more about JS Obsfucation!
One interesting thing what I notice is OneSignal being used. It’s a solution for push notifications, emails and so on. Now you know why random people start sending you notifications when you visit the site 😉.
<script src="https://cdn.onesignal.com/sdks/OneSignalSDK.js"></script>There are actual comments by people!
It’s disappointing, but those aren’t actual comments from facebook or actual humans!!!! They are just static comments from humans having random names.
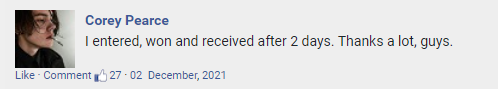
My friend Corey actually won an IPhone!
Atleast I’m happy for Corey, it’s been a week and I’m still waiting 😐.
Enough audit for today!
Now you know when you get presents either from Amazon or someone else, make sure to double check the link and don’t be too excited about it. See y’all in the next article.
Comments
You can write to me at [email protected]. Email services are insecure, consider encrypting emails with my PGP Key if you're sending me something sensitive.
Loading comments